Windows
Ligament 2FA client for Windows x64.
Download MSIProtect Windows Logon, RDP, RADIUS VPN/Wi-Fi, and Web SSO in a single Docker container. Instant 0.4s approval via push number matching — zero SMS or manual code typing.
Choose a scenario to see its route, second factor and behavior during a connectivity outage.
Arrows show request or connection initiation; responses use the same channel. MFA factors are alternatives, not a required sequence.
Scroll horizontally or adjust the zoom ↔
External portal: HTTPS + 2FA. App → Core: HTTPS / WSS. Relay → Core: a separate outbound WSS tunnel for the branch.
SSO and Windows Logon/UAC do not go through Relay. During a complete WAN outage cached Wi-Fi authentication stays local; the remote RDP/SSH tunnel to Core is unavailable.
Examine the real risks of foreign clouds, the friction of free TOTP apps, and the resilience of On-Premise Ligament.
Security that satisfies CISOs, saves capital for CFOs, and eliminates user friction.
Full data sovereignty. Complete compliance with enterprise security baselines and immutable audit logs.
Reduce 5-year Total Cost of Ownership (TCO) by up to 85% compared to foreign SaaS providers.
Deployment in 2 minutes without complex clusters. Ready GPO ADMX templates and silent MSI rollouts.
Zero external telemetry, clean code, transparent architecture, and direct technical engineering support.
Switch between the primary protection vectors of your enterprise perimeter.
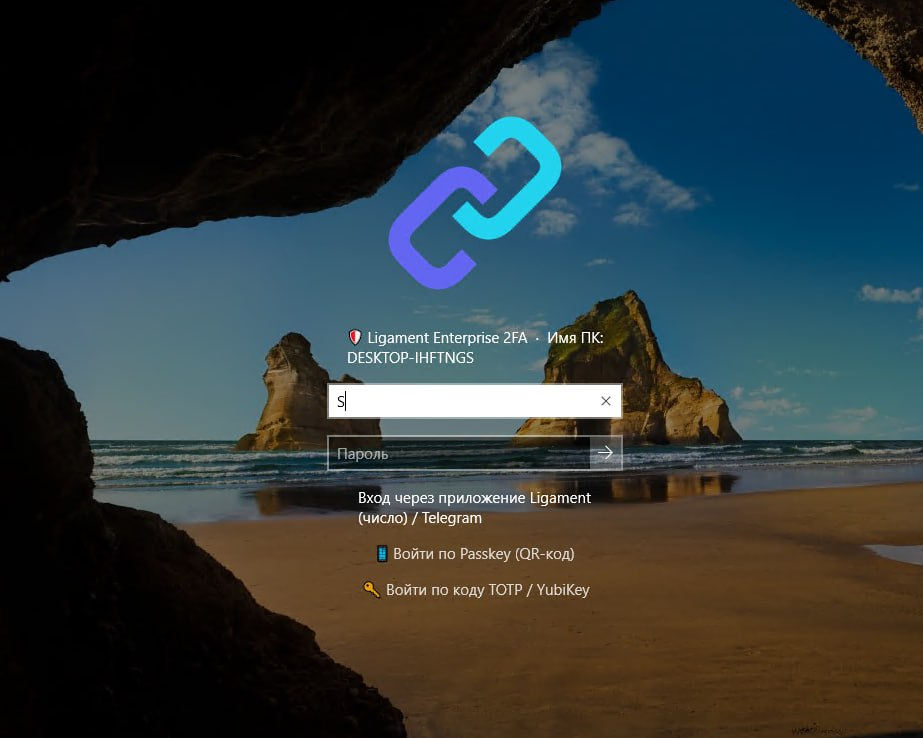
Вход на рабочий стол без повторного клика и нажатия Enter сразу после подтверждения на телефоне.
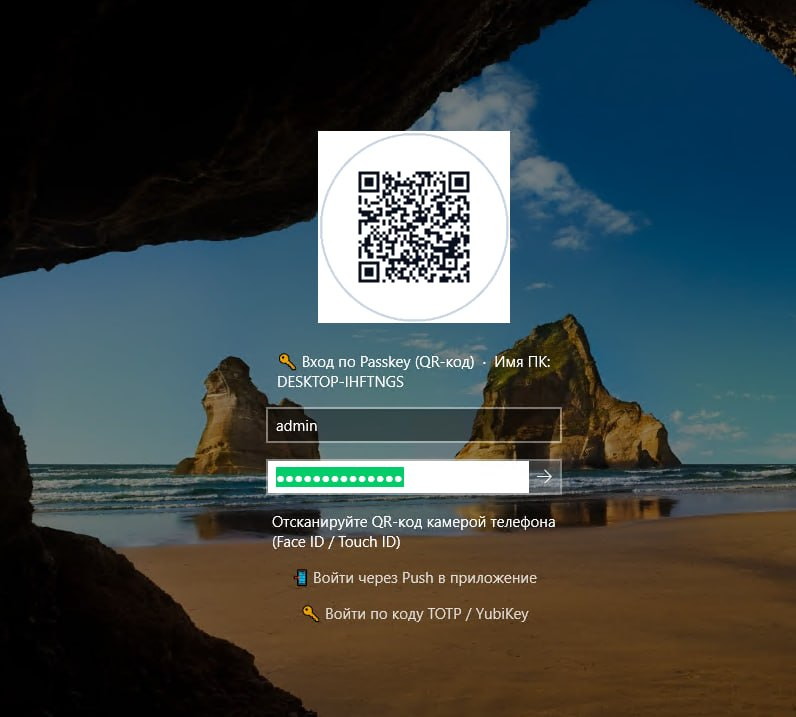
На экране входа отображается проверочное число. Защищает от push-бомбинга и случайных нажатий.
Запрос второго фактора на телефон администратора при попытке запуска программ с правами администратора.
Сервер удерживает UDP-сессию на время подтверждения вторым фактором, предотвращая повторные запросы.
Бесшовный доступ к корпоративному Wi-Fi WPA2/WPA3-Enterprise с аутентификацией пользователей.
Совместимость с MikroTik RouterOS, Cisco ASA, Fortinet, UniFi, WireGuard и OpenVPN.
Central Web SSO for corporate services such as Nextcloud, GitLab, Bitrix24 and 1C. OIDC/SAML 2.0 authentication runs strictly through Ligament Core; Branch Relay is not involved.
Forward RDP and SSH through Ligament Core or a branch Relay to the target host with 2FA confirmation. Provides protected remote access to workstations and servers.
Protect legacy web panels and internal systems through the central Core without changing their source code.
The Relay opens an outbound WSS :443 tunnel to Core, forwarding RDP :3389 and SSH :22 to internal branch hosts without a public IP or exposed ports.
During a WAN or fiber cut, the local Relay serves cached 802.1X WPA2/WPA3 Enterprise Wi-Fi authentication autonomously.
RDP/SSH forwarding and Wi-Fi events are buffered locally and replicated to Core after connectivity returns. Relay does not handle Web SSO or Windows Logon.
Architecting unified on-premise Ligament Link, Link Recorder session archive with AI forensics, PACS turnstiles with Anti-Passback, and Bolid fire evacuation zone mapping.
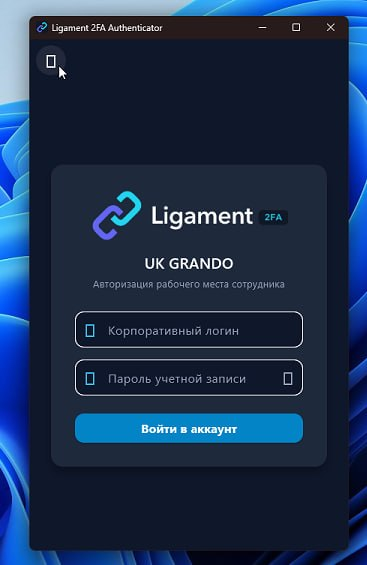
Workstation and RDP authentication: native LogonUI tile, instant Auto-Logon, Passkey verification via QR code and desktop companion client.
The latest stable release v1.1.73 is published in GitHub Releases. Choose your platform.
Ligament 2FA client for Windows x64.
Download MSINative installer for macOS.
Download DMGDEB, RPM and universal TAR.GZ packages for x86_64.
Choose packageAPK signed with the official release key.
Download APKiOS application package from the release.
Download IPABase — $1, Business with SSO — $2.50 per user/month. Annual billing gives 13 months of access. Perpetual Base — $15 per user one-time.
Paid licenses: minimum 20 users. Select 5 users for free Community.
Base and Business subscriptions: minimum 20 users; pay for 12 months and get the 13th free. Updates are included during the paid term. Business includes Trust, SSO, Bastion and basic SIEM event forwarding. Perpetual Base and separately purchased modules include 1 year of updates; optional annual update renewal is 20% of their license prices. The acquired version keeps working without renewal. Modules are purchased once, Relay per node. Support and deployment are separate.
Free base protection for up to 5 users: a second factor for Windows logon and UAC elevation, VPN and Wi-Fi authentication through RADIUS, and basic Notify notifications.
Subscription for Windows Logon/UAC, RADIUS VPN/Wi-Fi and Notify.
Base + SSO, Trust, Bastion and basic SIEM event forwarding. RDP/SSH access through Core or Relay to the host with 2FA.
Base license for each protected user: Windows Logon/UAC, RADIUS for VPN and Wi-Fi, and Notify notifications. Purchased once, with a perpetual right to use the acquired version.
Basic authentication event notifications help you follow user sign-ins and access. Included in the base license at no extra charge.
A branch node that opens an outbound WSS tunnel to Core and forwards RDP/SSH connections to internal hosts without a public IP. During WAN outages it maintains local Wi-Fi authentication through cached backup RADIUS. Each node requires its own license.
Device posture checks for access decisions: BitLocker, Microsoft Defender and the firewall. Helps consider workstation security alongside verification of the user’s identity.
Single sign-on to corporate web applications using OpenID Connect and SAML 2.0 with MFA. Users authenticate through Ligament Core; Branch Relay does not handle Web SSO.
Forward RDP and SSH through Ligament Core or a branch Relay to the target host with 2FA confirmation. Provides protected remote access to workstations and servers.
Advanced SIEM integration with an agreed scope. Basic event forwarding is included in Business and does not require the separate Advanced license.
Integrates Ligament with a physical access control system. Connects user identity verification with access to premises; compatibility with a specific system is determined during deployment.
Support service: scope, response times and SLA agreed in contract. Deployment quoted separately.
Discuss supportFeature-by-feature evaluation of enterprise authentication approaches.
Swipe or scroll right to compare all solutions ↔
| Feature / Parameter | Cisco Duo / Okta | Google Auth / TOTP | Ligament 2FA |
|---|---|---|---|
| 100% On-Premise (No Cloud) | ✕ (SaaS Cloud Only) | ✓ (Local) | ✓ 100% On-Premise in Docker |
| Windows Logon & UAC Protection | ✓ (Complex Setup) | ✕ (No Support) | ✓ Native LogonUI Credential Provider |
| 0.4s Auto-Logon | ✕ (Manual click required) | ✕ (Retype 6-digit code) | ✓ 0.4s Instant Auto-Logon |
| Branch Relay: RDP/SSH + Wi-Fi RADIUS | ✕ (Requires public IP / fails on WAN) | ✕ (No forwarding or sync) | ✓ WSS :443 forwarding + cached 802.1X Wi-Fi |
| Anti-Push Bombing Defense | Limited | ✕ (Vulnerable to phishing) | ✓ Mandatory Number Matching |
| Telegram & eXpress Bots | ✕ (No) | ✕ (No) | ✓ Zero App Installation Required |
| Cost for 100 Users | $7,200+ every year | $0 (Zero management) | Business: $3,000 for 13 months; perpetual Base: $1,500 one-time, modules extra |
From initial docker container launch to protecting domain workstations in under 15 minutes.
Spin up the container with a single command. Web administration and identity store are packaged inside.
Specify your domain controller or FreeIPA endpoint. Users and groups are mapped via LDAPS in 5 minutes.
Create a standard Active Directory GPO with ADMX templates for silent background workstation enrollment.
Clear technical and business answers to frequent inquiries.